The API Key Is Becoming The New Password
Machine credentials now connect cloud workloads, pipelines, SaaS platforms and AI agents. Treating them as configuration instead of governed identities creates long-lived access that may be more useful to an attacker than a password.
For years, cybersecurity focused heavily on passwords.
Weak passwords. Reused passwords. Stolen passwords. Phishing. Credential stuffing.
Then organisations strengthened authentication with MFA, password managers and better identity controls.
But while attention remained focused on human credentials, another category of credential quietly became more important.
API keys.
Service tokens.
Application secrets.
Machine credentials.
AI access tokens.
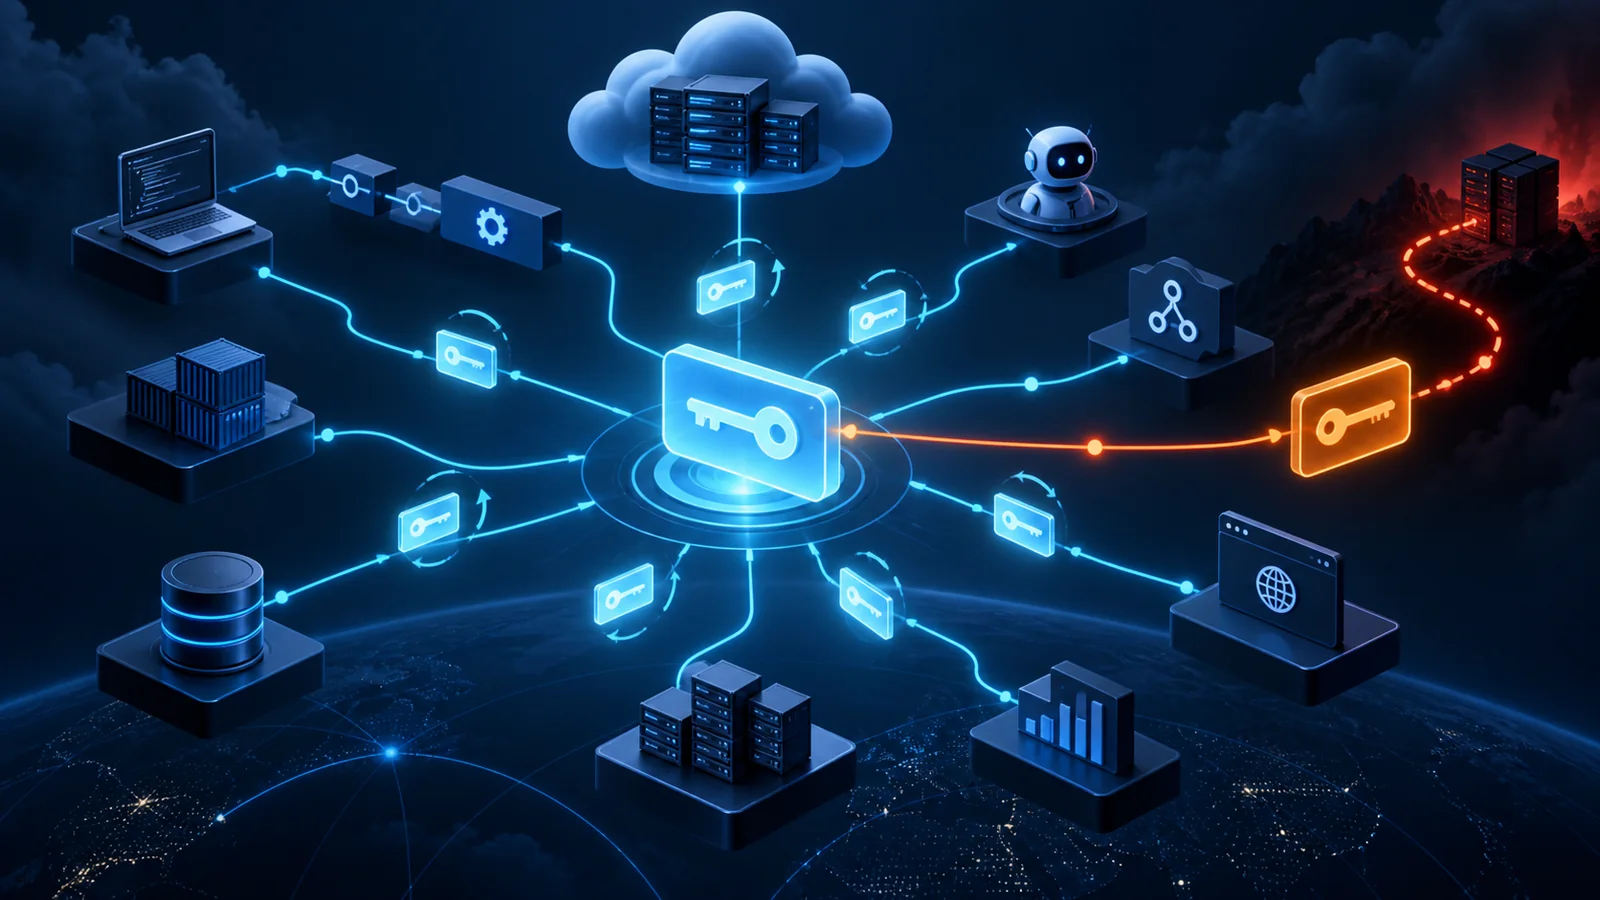
These credentials now sit behind cloud workloads, automation platforms, CI/CD pipelines, SaaS integrations and AI agents. In many environments, they may be more powerful than the passwords organisations spent years learning to protect.
Machines Need Identities Too
Modern enterprise environments are no longer built only around human users.
Applications talk to applications. Cloud workloads call APIs. Automation platforms access repositories. CI/CD pipelines deploy infrastructure. AI agents connect to external models and internal data sources.
Every one of these interactions requires trust.
And that trust is often represented by some form of machine credential.
An API key may look like a simple string, but architecturally it can represent access to data, services, infrastructure or AI capability.
That makes it an identity.
Just not a human one.
The Problem Is That API Keys Are Often Treated Like Configuration
Passwords are usually recognised as sensitive.
API keys are sometimes treated differently.
They are stored in configuration files, embedded in scripts, placed in environment variables, copied into pipelines, shared between teams and left unchanged for years.
Sometimes nobody is entirely sure who owns them.
That creates a dangerous gap.
A credential can be extremely powerful while receiving very little governance.
And unlike a human password, an API key may operate continuously without anybody noticing.
Not Every API Should Use The Same Credential Model
One of the most common architectural mistakes is treating every API connection the same way.
A public customer-facing API has different risks from an internal workload API.
A CI/CD pipeline should not authenticate the same way as a mobile application.
A high-trust system-to-system integration should not automatically rely on a long-lived static key simply because it is easy to configure.
Different scenarios need different trust models.
For example, a customer-facing application may use OAuth 2.0 and OpenID Connect because the access is tied to a user identity and delegated permissions.
An internal cloud workload may be better served by a workload identity or managed identity, avoiding the need to store a static secret at all.
A high-trust system-to-system connection may use mutual TLS, where both sides prove their identity using certificates.
A CI/CD pipeline should ideally use short-lived tokens rather than permanent deployment credentials.
A third-party SaaS integration may still require an API token, but that token should be tightly scoped, time-bound where possible and monitored.
The architecture should choose the authentication pattern based on the scenario.
Not convenience.
A Stolen API Key Can Be More Useful Than A Password
A stolen password may still encounter MFA.
A stolen API key may not.
If the key is valid and the service accepts it, the attacker may immediately inherit the permissions attached to it.
That could mean access to cloud resources, AI models, databases, repositories, internal APIs, automation platforms or third-party services.
The attacker does not need to impersonate a person.
They simply impersonate the application.
That changes the identity-security problem.
API Gateways Matter Because They Centralise Control
Another important design choice is where APIs are exposed.
An API Gateway can provide a central control point for authentication, rate limiting, schema validation, logging, throttling and policy enforcement.
This is especially useful where many services would otherwise expose their own inconsistent controls.
But centralisation also creates concentrated trust.
If every API depends on one gateway, that platform becomes critical infrastructure.
It must therefore be hardened, monitored and protected like any other high-value control plane.
The same principle applies everywhere in modern architecture.
Centralisation improves consistency.
It also increases blast radius when the central control fails.
AI Is Making Machine Credentials More Important
The growth of enterprise AI will accelerate this issue.
AI agents need access to data.
They need APIs.
They need service identities.
They need tokens to call models, retrieve documents, query databases or execute workflows.
That creates a rapidly growing number of non-human identities.
The question is no longer simply:
“Who has access?”
It is increasingly:
“What has access?”
And that is much harder to govern.
An AI agent that summarises documents does not need administrative access.
An AI agent that creates a service ticket does not automatically need permission to close it.
An AI assistant that reads internal knowledge does not need access to every repository.
The same least-privilege principle applied to human users must apply to machines.
Probably more strictly.
Webhooks Create Another Trust Problem
Webhooks are useful because they allow one system to notify another when something happens.
A payment completes.
A ticket changes.
A new user is created.
A deployment finishes.
But a webhook endpoint is still an entry point.
If it accepts requests without strong validation, an attacker may be able to trigger actions by sending fake events.
Good webhook architecture should therefore include signed requests, replay protection, source validation and strict control over what the receiving system is allowed to do.
Again, the issue is not the API technology itself.
It is the trust model around it.
Long-Lived Credentials Create Long-Lived Risk
One of the biggest weaknesses with API keys is longevity.
A password may expire.
A user may leave.
An account may be disabled.
But an API key can remain active for months or years if nobody owns its lifecycle.
That is convenient operationally.
It is also risky.
A good machine-identity architecture should therefore ask:
Who owns this credential?
Why does it exist?
What can it access?
Where is it stored?
How often is it rotated?
Can it be revoked quickly?
Is its usage monitored?
If those questions cannot be answered, the credential is not being governed.
Secrets Management Is Not The Same As Identity Governance
A secrets vault is useful.
But storing a credential securely does not answer whether the credential should still exist.
That requires governance.
Machine credentials need ownership, lifecycle management, rotation, access review, monitoring and revocation.
This is where traditional identity governance must expand.
Joiners, movers and leavers are no longer only human concepts.
Applications change.
Services are retired.
Workloads move.
AI agents are created.
Integrations disappear.
Machine identities need lifecycle management too.
Final Thoughts
The password is not disappearing.
But it is no longer the only credential that matters.
Modern organisations increasingly depend on API keys, tokens, certificates, workload identities and application secrets to keep systems connected.
Those credentials may never be typed by a human.
But they can still unlock critical systems.
That is why the next identity-security challenge may not come from an employee clicking a phishing link.
It may come from a forgotten API key sitting inside a script, pipeline, webhook integration or AI workflow.
We spent years teaching people to protect passwords.
Now we need to apply the same discipline to credentials that belong to machines.
And perhaps one more principle.
Do not ask only whether an API is secure. Ask whether its identity model is appropriate for the trust it carries.
Because the API key is becoming the new password.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.