The PHP2Shell Lesson Is Not Just Patch Faster. Know What You Are Running.
A critical vulnerability in a common runtime exposes more than a patching problem. It tests whether the organisation can immediately identify affected systems, owners, exposure and blast radius.
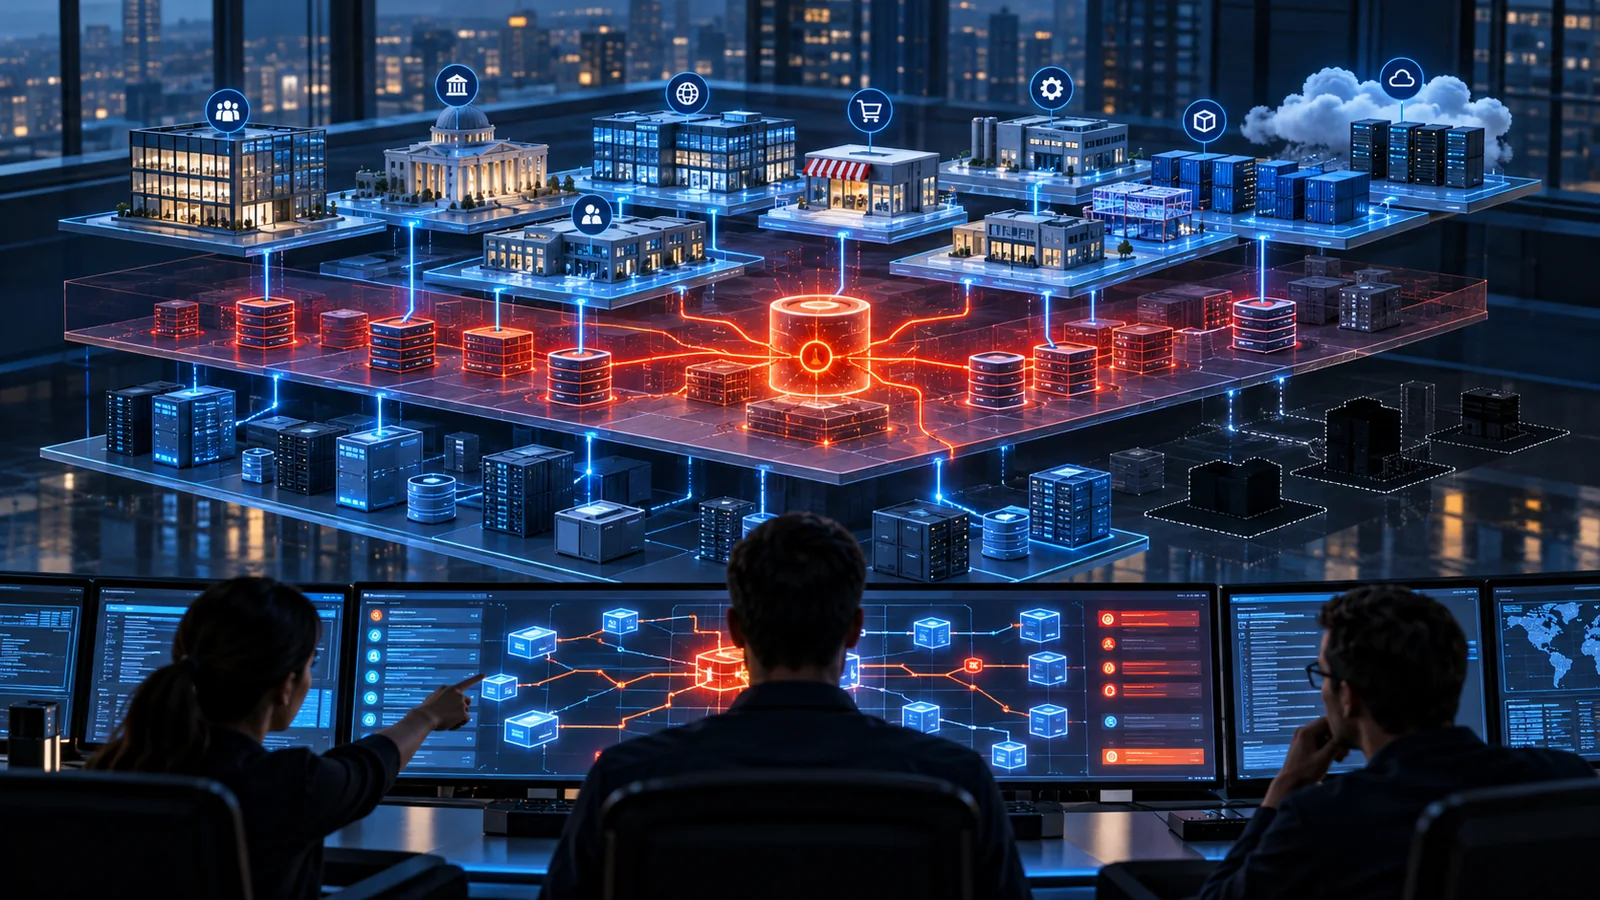
On 21 October 2026, the PHP project released emergency security updates for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively referred to as PHP2Shell. Both can allow unauthenticated remote code execution in affected PHP web environments, and the PHP security advisory states that there are no complete mitigations: updating is the safe option.
The technical severity is obvious. Remote code execution in a widely deployed web runtime deserves urgent attention.
But there is a more important enterprise lesson.
When a critical vulnerability appears in something as common as PHP, the first security question should not be “Do we have a patch?” It should be “Can we immediately tell where we are exposed?”
That is a very different capability.
A Vulnerability Becomes An Incident Problem When Visibility Is Weak
PHP is not necessarily something every business owner thinks about.
It may sit underneath a public website, an old internal portal, a vendor product, a content management system or an application that has been running quietly for years.
That is precisely why vulnerabilities in common technology stacks can be difficult to manage.
NACSA's advisory notes that affected runtimes can include PHP-FPM, Apache mod_php, PHP-CGI, LiteSpeed and FrankenPHP, while PHP 8.1 and older are already unsupported upstream.
An organisation may therefore know that PHP is vulnerable before it knows how much PHP it actually has.
That gap matters.
If it takes days to answer which internet-facing systems use the affected runtime, which version they run, who owns them and whether the application can be safely upgraded, then the vulnerability-management problem began long before the CVE was published.
It began with asset visibility.
The Lesson Is Similar To Shellshock
I made a similar argument in Shellshock Was Patched Years Ago. Residual Risk Is a Governance Problem.
A vulnerability can be technically well understood and still remain an organisational risk because nobody owns the remaining exposure, unsupported technology continues operating, or an exception quietly becomes permanent.
PHP2Shell creates the same reminder.
Patching is important.
But vulnerability management is not simply a race between a CVE announcement and a patch-management tool.
It is also about whether the organisation knows what it owns, whether those systems have accountable owners, whether unsupported versions have been eliminated and whether emergency remediation can be performed without weeks of dependency analysis.
Internet-Facing Does Not Mean “Just A Web Server”
The vulnerabilities are particularly serious because an unauthenticated attacker may be able to execute code with the privileges of the PHP web worker. The flaws exist in the PHP engine itself rather than necessarily in the application's business code.
That distinction is important.
An application team may have followed secure coding practices.
The application may have passed penetration testing.
The WAF may be configured.
The development team may not have introduced the vulnerability at all.
Yet the runtime underneath the application can still create the exposure.
This is another reason security architecture must understand the complete technology stack rather than assessing only the application visible to the user.
Runtime.
Framework.
Libraries.
Operating system.
Container image.
Reverse proxy.
Middleware.
Every dependency becomes part of the attack surface.
This connects directly with Attack Surface Is Designed Long Before Go-Live. Attack surface is not only the functionality developers intentionally expose. It also includes the technology required to make that functionality run.
Unsupported Technology Turns Urgency Into A Crisis
The PHP advisory also highlights another familiar issue.
PHP 8.2 reaches end of life on 31 December 2026, while PHP 8.1 and older are already outside upstream support.
That makes lifecycle management part of cybersecurity.
An organisation running a supported version can patch.
An organisation running an unsupported version may first need to determine whether the application can even move to a supported branch.
That difference can turn an emergency patching exercise into an application-modernisation problem.
Security teams often discover technical debt at the worst possible moment: when attackers are already interested in exploiting it.
This is why end-of-life technology should not be treated merely as an operational hygiene issue.
It is future incident exposure.
Prioritisation Matters More Than The Number Of Findings
When a vulnerability this severe appears, organisations may discover hundreds of affected assets.
Treating them all equally is not useful.
The first priority should be understanding exposure and business consequence.
Which systems are internet-facing? Which contain sensitive information? Which runtime configuration creates the highest exposure? Which applications have privileged connectivity to internal systems? Which compromised web server could become a route towards something more important?
The UK NCSC and ENISA both advise organisations to identify affected applications and prioritise remediation, particularly for externally exposed systems.
This is where vulnerability management should connect with architecture.
A vulnerable PHP server isolated inside a tightly constrained environment represents a different risk from a vulnerable server that can communicate freely with databases, internal applications and privileged management services.
The CVE may be identical.
The blast radius is not.
As discussed in The Strongest Architecture Is The One That Limits Blast Radius, architecture determines how much damage the initial compromise is allowed to create.
Patching Is Necessary. Vigilance Is Broader.
The right response to PHP2Shell is to patch affected supported versions urgently. For systems that cannot immediately be updated, isolation and exposure reduction may be necessary while remediation is completed.
But once the emergency passes, organisations should ask harder questions.
How quickly did we know we were affected? Did our asset inventory identify the runtime and version? Did we know which applications were externally exposed? Did each application have an accountable owner? Could we prioritise systems based on business impact and attack path? Were unsupported versions already known? Could we isolate vulnerable systems while keeping critical services operating?
Those questions measure security readiness better than simply recording how many patches were eventually installed.
Security Controls Cannot Replace Technology Hygiene
There is always a temptation to compensate.
Perhaps the WAF can block the exploit.
Perhaps EDR will detect post-exploitation activity.
Perhaps SIEM will generate an alert.
Those controls are valuable, but they should not become excuses for leaving the vulnerable runtime in place when a security update exists.
This is the same principle discussed in Security Controls Cannot Fully Repair Poor Architecture.
Compensating controls can reduce exposure.
They do not remove the vulnerable condition.
And in this case, the PHP project itself states that updating is the safe choice.
Final Thoughts
PHP2Shell will eventually become another entry in vulnerability databases.
Patches will be deployed. Scanners will stop reporting the affected versions. Attention will move to the next critical vulnerability.
The more valuable lesson should remain.
A mature organisation should be able to move quickly from:
A critical vulnerability exists
to:
We know where it exists, who owns it, how exposed it is, what it can reach, how quickly we can isolate it and when it will be remediated.
That capability cannot be created on the day the vulnerability is announced.
It comes from asset visibility, lifecycle management, architecture awareness, clear ownership and continuous vigilance established beforehand.
The security community will continue discovering critical vulnerabilities.
We cannot control when the next one appears.
We can control how surprised we are when it does.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.