Three-Tier Architecture Was Built for Yesterday. Future Architecture Must Be Designed to Survive.
Three-tier architecture still explains applications, but it cannot describe the cloud-connected, identity-centric and AI-enabled enterprise. Future architecture must remain defendable when something is compromised.
For decades, enterprise applications were easy to explain through three familiar tiers: presentation, application and database.
The model was useful because most systems were built around relatively predictable boundaries. Users entered through a front end, application logic ran in the middle and data remained behind another layer of protection.
That model is not wrong.
It is simply no longer enough to describe the enterprise we are building.
Organisations are moving workloads into cloud environments, consuming SaaS, exposing APIs, connecting business partners, deploying AI assistants and agents, and increasingly depending on identities that do not belong to humans. At the same time, architecture must prepare for AI-assisted attacks, supply-chain compromise and a future where some of today's cryptographic assumptions may no longer be sufficient.
The architecture of the future therefore needs to do more than organise applications.
It needs to remain defendable when something is compromised.
From Application Tiers To Enterprise Capabilities
The next generation of architecture should not simply replace three tiers with more tiers.
It should describe the enterprise according to the capabilities that now need to work together.
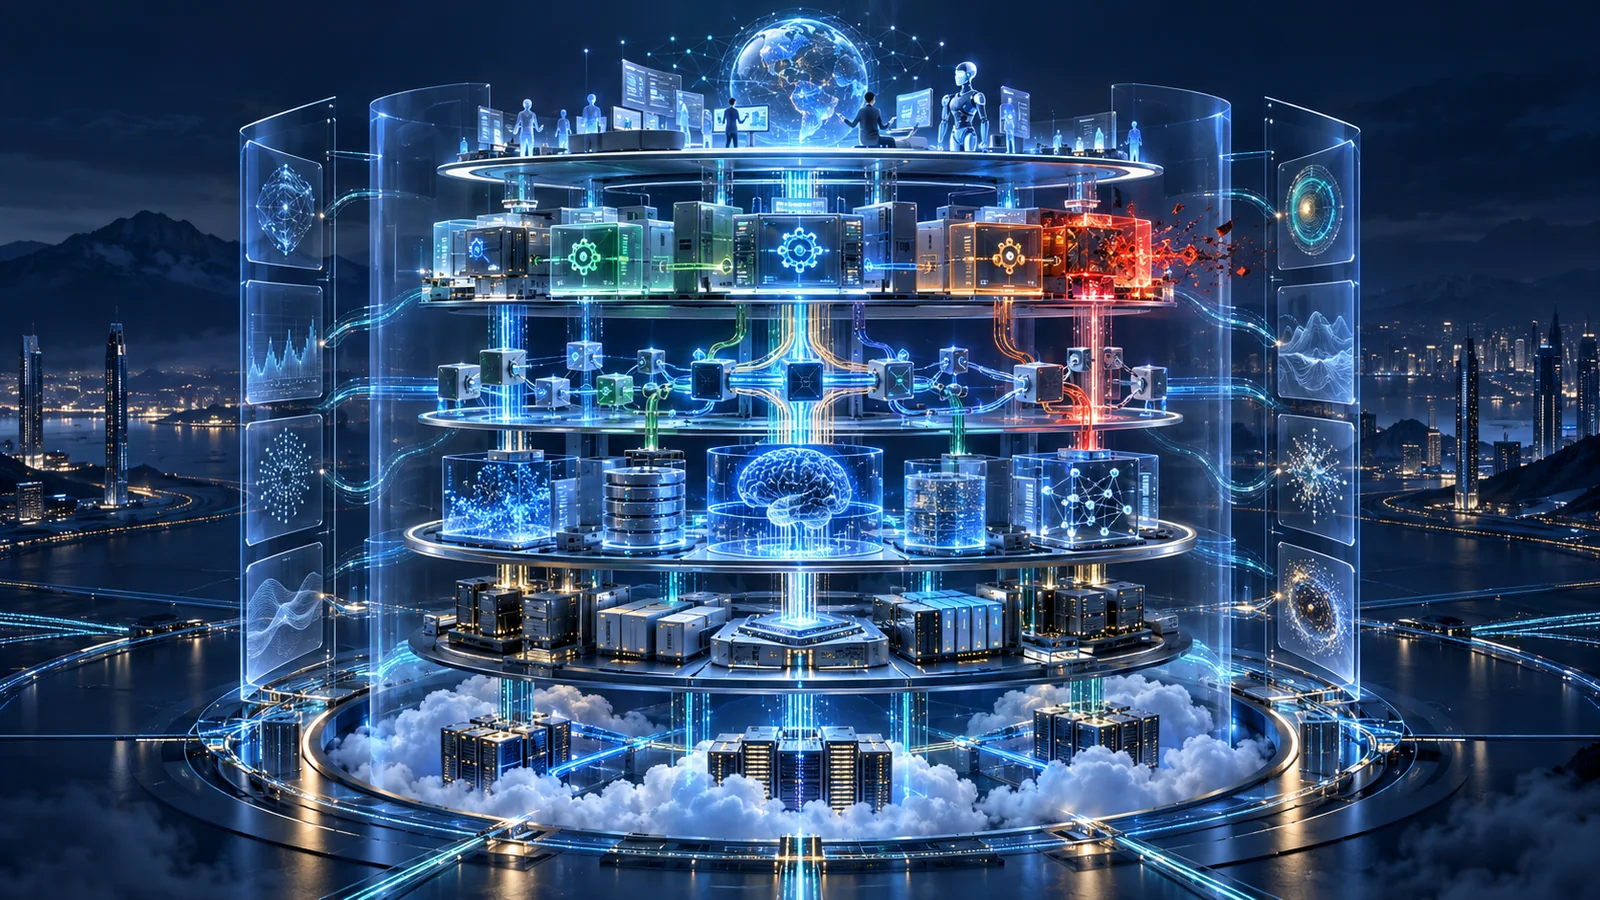
I would frame this as a Next-Generation Defendable Architecture built around six functional layers: Digital Experience & Agent, Business Capability & Orchestration, Integration, API & MCP, Data, Intelligence & AI, Platform & Shared Services, and Cloud & Infrastructure Foundation.
These layers describe how modern digital services are actually delivered.
Users and AI agents interact through the experience layer. Business processes and orchestration determine what should happen. APIs, events, middleware and MCP provide connectivity. Data and AI create intelligence. Shared platforms provide common technology capabilities. Cloud and infrastructure provide the foundation underneath them.
But the important difference is that security should not become a seventh layer sitting underneath everything else.
Trust, security and resilience must run through every layer.
Trust Must Be Designed Across The Architecture
Modern systems increasingly depend on relationships rather than physical location.
A user trusts an application. An application trusts an API. An API trusts another service. An AI agent trusts an MCP server. A business platform trusts an external provider.
As discussed in Every Trust Relationship Is An Attack Path, every connection should also be understood as a trust decision.
Future architecture therefore needs to make those relationships visible.
Who is communicating? What identity is being used? What authority is being granted? What data can cross the boundary? How long should that trust exist? What happens if either side becomes compromised?
An architecture diagram that only shows connectivity is increasingly incomplete.
The arrows need to represent trust.
Identity Becomes A Common Control Across Every Layer
Three-tier architecture often assumed that the network provided much of the security boundary.
That assumption is becoming increasingly difficult to maintain in cloud environments.
Users work remotely. Workloads are created dynamically. APIs communicate across different platforms. SaaS sits outside the traditional enterprise perimeter. AI agents may perform actions without an interactive human session.
This is why the new security perimeter is no longer the network; it is identity.
Identity must follow the transaction through the architecture.
Human identities, privileged accounts, workload identities, service accounts, API credentials and AI agents should all have explicit ownership and limited authority.
A request should not become trusted simply because it originates from a familiar network.
It should be trusted because the identity, context and requested action justify that trust.
AI Should Be Embedded, Not Bolted On
AI should not become another isolated architecture layer.
It will appear throughout the enterprise.
AI assistants may sit in the Digital Experience layer. AI may support decisioning inside business capabilities. AI Gateways and MCP may operate within the integration layer. Models, RAG platforms and vector stores may sit within the Data, Intelligence & AI layer. Model runtimes and supporting services may depend on shared platforms and cloud infrastructure.
That means AI security must also work across the architecture.
The organisation needs to govern which models are approved, which data they can access, which MCP servers they can call, which tools they may invoke and how much authority an agent receives.
This is exactly why the architecture around AI matters more than simply asking whether the model itself is secure.
AI capability can be broad.
AI authority should remain narrow.
Cloud Should Reduce Blast Radius, Not Recreate The Data Centre
Moving to cloud should not mean rebuilding the old enterprise network inside somebody else's infrastructure.
Cloud provides an opportunity to create smaller and more explicit security domains.
Production can be separated from non-production. Critical workloads can have dedicated boundaries. Privileged identities can be isolated. Applications can use workload identities rather than shared credentials. Data access can be restricted to specific services.
The objective is simple: if one component is compromised, the attacker should not automatically inherit everything around it.
This connects directly to The Strongest Architecture Is The One That Limits Blast Radius.
The strength of the architecture is not measured only by whether compromise can be prevented.
It is also measured by how far the compromise can travel.
Quantum Readiness Is An Architecture Problem
Quantum computing creates another reason architecture must evolve.
The immediate issue is not that every cryptographic control suddenly becomes useless. The more practical problem is that organisations have large quantities of cryptography embedded inside applications, APIs, certificates, software libraries, infrastructure and data protection mechanisms.
Many organisations do not even know where all of it exists.
That creates a future migration problem.
A defendable architecture should therefore support crypto agility. Algorithms, certificates and key-management mechanisms should be replaceable without requiring the entire application to be redesigned.
The organisation should know which information needs long-term confidentiality, where cryptography is being used and how quickly affected components could move to post-quantum alternatives when required.
Quantum readiness should therefore not become a standalone technology project.
It should become part of architectural lifecycle management.
Resilience Must Exist At Every Layer
Traditional disaster recovery often focuses heavily on infrastructure.
Servers fail, so another server is restored. A data centre becomes unavailable, so workloads move elsewhere.
Cyber recovery is different.
The infrastructure may still be available while the environment itself can no longer be trusted.
An attacker may control identities. Configuration may have been changed. Credentials may be compromised. Data may have been corrupted. Malware may exist inside backups.
Future architecture therefore needs resilience at every functional layer.
The customer channel may require an alternate operating mode. Critical business processes may need to continue with reduced functionality. External integrations may need to be isolated quickly. Critical data must have protected and verifiable copies. Shared platforms should be reproducible from trusted configurations. Cloud infrastructure should be capable of being rebuilt into a known-good state.
Recovery is no longer simply:
How quickly can we restore the technology?
The better question is:
How quickly can we restore a business service into an environment we can trust?
Defendable Architecture Changes The Design Question
This is where Defendable Architecture should differ from conventional enterprise architecture.
Traditional architecture asks whether the components work together, whether the design scales and whether it supports the required business capability.
Defendable Architecture adds another set of questions.
What happens when one component is compromised? Can the attacker cross the next trust boundary? Can the affected service be isolated without bringing down everything else? Can critical business functions continue? Can the environment be recovered without trusting the same identities and systems that may have been compromised?
This changes the design philosophy.
Architecture should not only optimise how systems work together.
It should also design how systems fail apart.
That is an important distinction.
Final Thoughts
Three-tier architecture is not dead. Applications will continue to have interfaces, logic and data.
But enterprise architecture has moved far beyond those three concerns.
The future enterprise is cloud-based, API-connected, data-driven, identity-centric and increasingly AI-enabled. Its threat environment will include faster AI-assisted attacks, compromised trusted partners, software supply-chain attacks and eventually changes to the cryptographic foundations on which digital trust depends.
A Next-Generation Defendable Architecture should therefore organise the enterprise around modern functional capabilities while embedding three principles across all of them: trust and identity, security and observability, and resilience and recovery.
Identity must be explicit. Trust must be constrained. AI authority must be limited. Cryptography must be replaceable. Compromise must have a small blast radius. Recovery must restore trust, not merely technology.
The architecture of yesterday was primarily designed to make systems work.
The architecture of tomorrow must also be designed to survive when they do not.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.