Cyber Threat Levels Matter Only If They Trigger Different Defences
Malaysia's national cyber threat level is Moderate. The classification matters only if organisations know exactly how their defensive posture should change when the external threat changes.
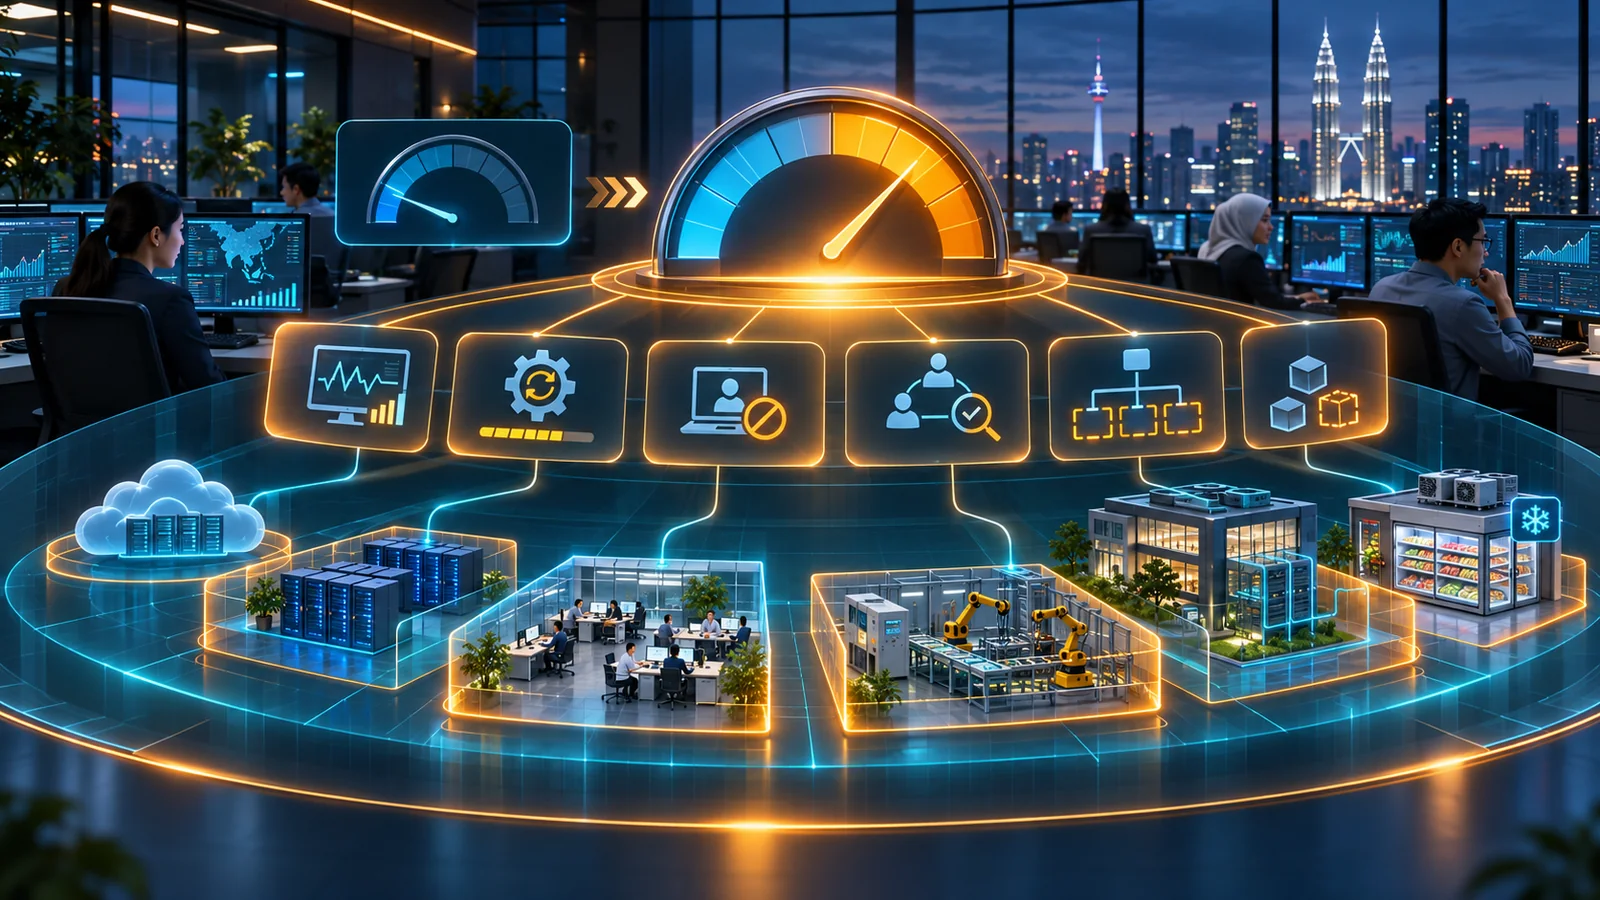
Malaysia's national cyber threat level has been elevated to MODERATE.
That should mean more than changing the colour on a dashboard.
A threat level is useful only if it changes behaviour.
If the security team monitors exactly the same way, patches at the same speed, reviews the same assets and maintains the same response posture regardless of whether the threat level is Low, Moderate, Caution, High or Critical, then the classification has limited operational value.
The important question is therefore not:
“What is the current threat level?”
It is:
“What are we doing differently because the threat level changed?”
Threat Levels Should Trigger Predefined Actions
A national threat-level framework provides organisations with an indication that the external threat environment has changed.
At a Moderate level, cyber threats or known exploits may already be present, even if the wider national impact remains limited.
That should trigger a corresponding change inside the organisation.
Monitoring may need to become more focused. Internet-facing assets may need additional verification. Vulnerability remediation may need to accelerate. Threat intelligence should be correlated against the organisation's own technology footprint. Third-party connectivity may require closer scrutiny.
The exact response will differ between organisations.
But the principle should remain the same.
A change in external threat should create a change in internal defensive posture.
The European Refrigeration Attacks Show Why This Matters
The recent attacks against supermarket refrigeration systems across Europe are a useful example.
During October and early November 2026, attackers remotely manipulated internet-connected refrigeration controllers across several European countries. Refrigerators and freezers were forced into defrost modes or had temperature settings changed, causing businesses to discard large quantities of food.
The most recent wave affected retailers across countries including Belgium, Sweden, Luxembourg, Ireland and Estonia. Some systems were reportedly pushed to temperatures around 50°C. A Polish government public-health notice described a second wave beginning on 2 November across at least ten European countries and warned of remote configuration changes that raised temperatures to 40–50°C.
The technology being attacked was not exotic.
CERT-FR's alert identified numerous compromises of remote refrigeration controllers from several vendors. It warned against exposing management interfaces directly to the internet and recommended secure VPN or protected-network access, firmware updates and replacement of default passwords.
That creates an important question.
If an attack pattern is already visible elsewhere, when should another organisation change its posture?
Before it becomes the next victim?
Or after?
Threat Intelligence Has Value Only When It Changes Priorities
Security teams consume a large amount of threat intelligence.
New vulnerabilities.
New attack techniques.
New malware.
New campaigns.
New exploited products.
But intelligence without action easily becomes information overload.
Suppose intelligence indicates that attackers are actively targeting a particular type of internet-connected operational technology.
A useful response is not simply forwarding the advisory to several distribution lists.
The organisation should immediately ask whether it operates the same technology, whether those systems are externally reachable, whether known vulnerabilities remain unpatched and what business process depends on them.
That is what turns threat intelligence into security posture.
The discussion in The PHP2Shell Lesson Is Not Just Patch Faster. Know What You Are Running. made a similar point. The ability to respond quickly depends heavily on knowing what technology exists, where it is exposed and who owns it.
The alert should not start the discovery process.
It should trigger a response using information the organisation already maintains.
Critical Assets Should Receive Different Treatment
The European fridge attacks also demonstrate that cyber impact does not always begin with data theft.
The attacker changed physical conditions.
Food spoiled.
Retail operations were disrupted.
Business losses occurred.
The connection between cybersecurity and business operations became very direct.
For NCII and other organisations operating critical services, this matters.
Operational technology, IoT systems, building-management systems, sensors, remote controllers and other connected infrastructure should not be viewed as secondary IT assets simply because they do not store customer databases.
If compromise can interrupt an important business capability, the asset is security relevant.
The architecture should understand what the device controls, what networks it can reach, who administers it, how it is updated and whether remote connectivity is genuinely required.
The attack surface exists wherever digital access can create physical or business impact.
Moderate Should Not Mean Panic
Changing security posture does not mean treating every elevated threat level as an emergency.
The objective is not to create constant crisis mode.
The objective is to have predefined defensive states.
For example, a Moderate posture could trigger stronger monitoring of internet-facing assets, verification of critical vulnerabilities, review of high-risk remote access, increased scrutiny of privileged activity and confirmation that critical third-party connections remain secure.
A High posture might introduce additional restrictions, temporary hardening measures, more frequent threat hunting, changes to administrative access and greater readiness to isolate affected environments.
A Critical posture may require war-room operations, heightened containment authority and explicit business continuity measures.
The specific actions should be determined before the threat level changes.
Otherwise valuable time will be spent deciding what the new posture actually means.
Posture Should Include Third Parties
Threat posture cannot stop at the organisation's own perimeter.
Modern businesses depend heavily on managed services, SaaS, cloud providers, maintenance vendors and external integration partners.
The European refrigeration incidents demonstrate this clearly. Refrigeration technology is frequently remotely managed, and the business may depend on technology and access maintained by external specialists.
That relates directly to Your Trusted Business Partner Is Compromised. Are You Next?.
When the threat environment changes, organisations should consider whether external connections require additional verification.
A partner may not yet be compromised.
But if attackers are actively targeting technologies used by that partner, the risk relationship has changed.
Architecture Determines How Much An Attack Can Hurt
Prevention remains important.
Patch the vulnerability.
Remove unnecessary internet exposure.
Change default credentials.
Secure remote management.
But architecture determines what happens when prevention fails.
Can an IoT controller communicate with other important systems?
Can a compromised building-management network reach corporate IT?
Can a third-party maintenance account access more systems than necessary?
Can the affected equipment be isolated while the business continues operating?
These questions connect directly with The Strongest Architecture Is The One That Limits Blast Radius.
The attacker may compromise one device.
Architecture determines whether that remains one-device compromise or becomes something much larger.
Monitoring Must Lead To Action
There is another lesson from the European incidents.
In some cases, businesses discovered the refrigeration problem because physical temperatures changed dramatically.
That is detection.
But mature security needs to detect abnormal activity before the business outcome becomes the alert.
Unexpected remote administration.
Unusual configuration changes.
Controllers communicating with unfamiliar destinations.
Repeated authentication attempts.
Changes to operational parameters outside normal maintenance windows.
Security monitoring should increasingly understand operational behaviour, not only malware signatures.
And when something abnormal is detected, there needs to be authority to act.
Disconnect the remote access.
Disable the account.
Isolate the device.
Suspend the integration.
That is where monitoring becomes defence.
Defendable Architecture Should Support Different Security States
This is also where Defendable Architecture becomes relevant.
Architecture should not assume that the environment operates permanently under one security posture.
The system should be capable of moving into a more defensive state when conditions change.
Remote access may become more restricted.
Higher-risk integrations may require additional verification.
Privileged activity may require stronger approval.
Internet-facing services may receive additional protection.
Non-essential connectivity may temporarily be removed.
The organisation should be able to increase security without redesigning the architecture during the incident.
That requires boundaries, visibility and control mechanisms to exist beforehand.
As discussed in Security Controls Cannot Fully Repair Poor Architecture, controls are most effective when the architecture already provides meaningful places to enforce them.
Final Thoughts
Threat levels are useful because they communicate that the environment around us has changed.
But the classification itself does not protect anything.
Protection comes from what the organisation does next.
A Moderate threat level should trigger a Moderate posture.
A High threat level should trigger stronger defensive measures.
A Critical threat level should place the organisation into a state designed for active containment and business survival.
Those actions should already be defined, exercised and understood before they are needed.
The recent attacks against connected refrigeration systems across Europe show why.
Attackers did not need futuristic AI or quantum computing.
They exploited ordinary connected technology and turned digital access into physical business impact.
Threat intelligence gave others an opportunity to learn from the first incidents before the attacks spread.
That opportunity only matters if someone acts on it.
Cyber threat levels matter only if they trigger different defences.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.