Your Trusted Business Partner Is Compromised. Are You Next?
A trusted partner can become an attacker’s route into your environment without defeating the perimeter. Security architecture must constrain third-party trust, limit blast radius and preserve the ability to isolate a compromised connection quickly.
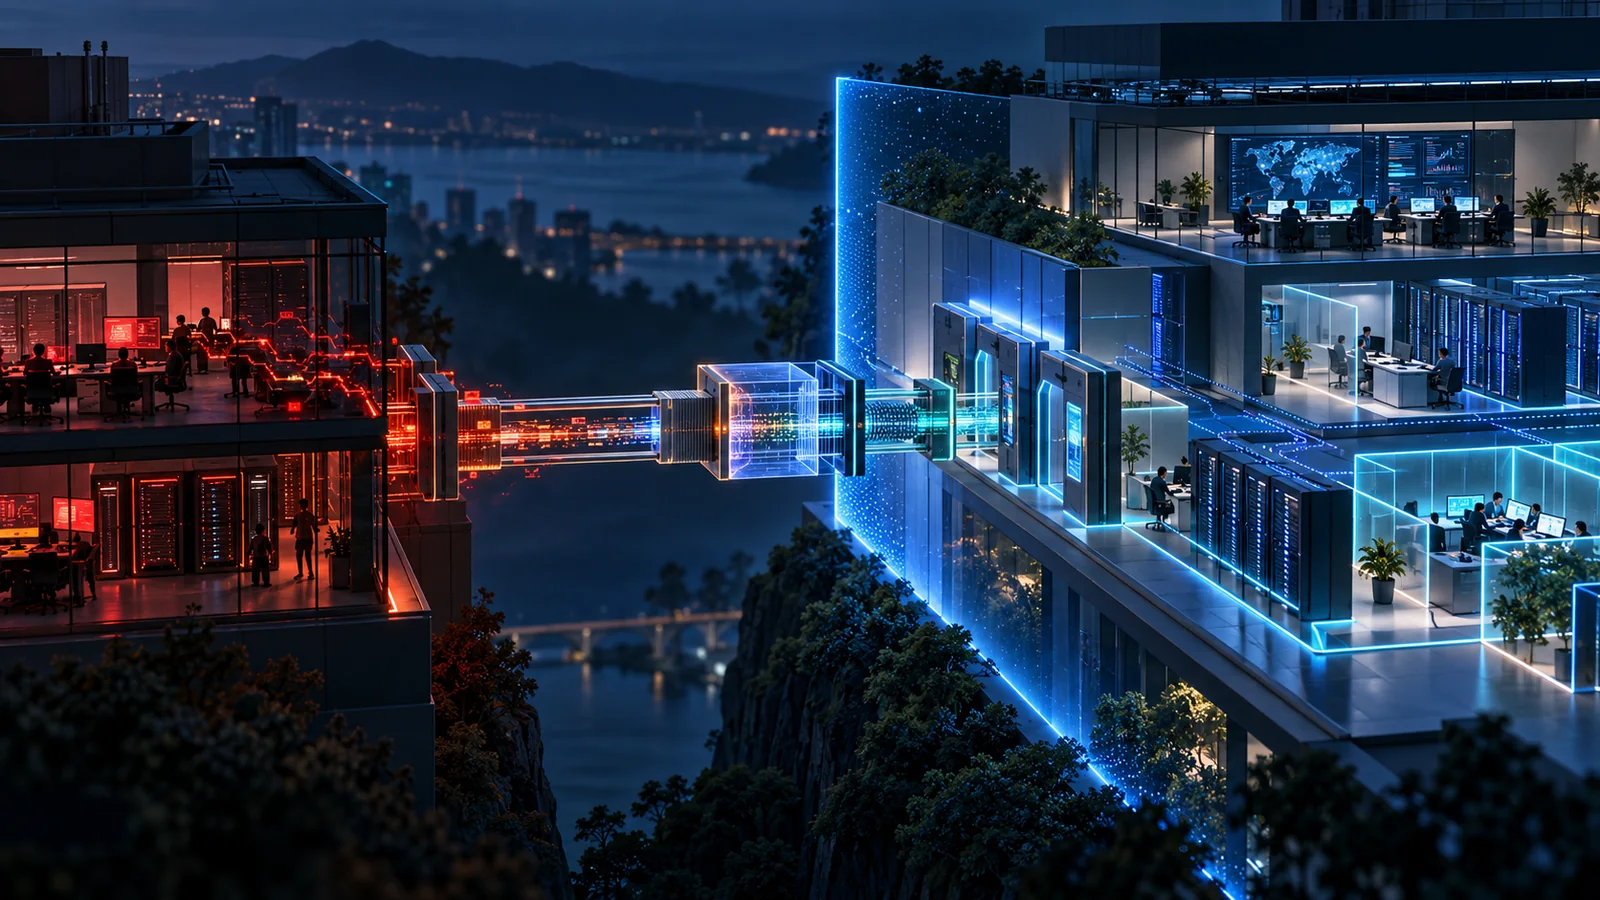
Cybersecurity architecture often focuses on protecting the organisation from external threats. Firewalls, endpoint protection, identity management, network segmentation and continuous monitoring are all designed to reduce the chance of an attacker getting in.
But modern organisations do not operate as isolated environments.
They exchange data with business partners, service providers, financial institutions, technology vendors and other external entities. These connections are essential for business operations, but they also create another kind of security problem.
What happens when the attacker does not need to break through your perimeter?
What if the attacker arrives through a connection you already trust?
When Trust Becomes An Attack Path
Imagine two organisations, Company A and Company B.
They have a legitimate system integration supporting normal business operations. The connection may use APIs, secure file transfer, middleware, private connectivity or dedicated service accounts.
Company B has already approved the relationship. Firewall rules are configured. Credentials are issued. The integration operates as expected.
Then Company A is compromised.
An attacker gains access to a server involved in the integration. From there, the attacker discovers API credentials, authentication tokens, service accounts or other access used to communicate with Company B.
The attacker now has an opportunity to interact with Company B through an established and trusted connection.
To Company B, the traffic may still appear legitimate because it originates from the expected partner environment and may even use valid credentials.
The question is no longer whether Company B has strong perimeter security.
The question is whether Company B can distinguish legitimate partner activity from malicious activity originating from a compromised partner.
Lateral Movement Can Cross Organisational Boundaries
Lateral movement is normally discussed as an attacker moving between systems inside one organisation.
But the same principle can extend across organisational boundaries.
A compromised integration server, trusted service account, VPN connection or remote administration channel can become a bridge into another environment.
A site-to-site VPN may encrypt traffic between two organisations, but encryption does not make a compromised endpoint trustworthy. An authenticated API may still accept malicious activity if the attacker possesses valid credentials.
A successful connection does not automatically mean a trustworthy connection.
This is why architecture should never assume that a trusted partner will remain trustworthy forever.
That does not mean one compromised organisation will automatically compromise another. The attacker still needs an exploitable weakness, excessive privilege, stolen credentials or an integration path that provides enough access.
But the possibility should be considered before the incident happens, not after.
The Hidden Risk Of Transitive Trust
The problem becomes more complicated when trust relationships extend beyond two organisations.
Company B trusts Company A.
Company A trusts a technology provider.
That provider may depend on another supplier, managed service provider or remote administrator.
Over time, these relationships create a chain of interconnected systems and identities.
This is transitive trust.
The risk is that one organisation may depend on the security posture of another organisation that depends on someone else entirely.
This is closely related to the principle discussed in Every Trust Relationship Is An Attack Path. A connection does not only provide business functionality. It creates a trust relationship that can potentially be abused if one side becomes compromised.
The more complex the ecosystem becomes, the more difficult it is to answer a simple question:
How much of your security depends on systems, identities and infrastructure that you do not directly control?
Third-party assessments, contracts and security questionnaires are still important, but they cannot guarantee that a partner will never be compromised.
Architecture must therefore assume that a trusted connection may eventually become hostile.
Design For Compromise, Not Just Connectivity
External integration should not be treated only as a technical connectivity requirement.
It should also define the security boundary around that connectivity.
The objective is not to stop organisations from integrating. The objective is to make the integration resilient when trust fails.
A strong design starts by eliminating unnecessary implicit trust. A business relationship should not automatically provide broad technical access. Every connection should be authenticated, authorised and limited to its intended purpose.
Integration services should also be isolated where possible. External connectivity should terminate in a controlled integration zone rather than exposing critical internal systems directly.
Privileges should be minimal. API credentials, service accounts and integration identities should have only the permissions required for the specific function they perform.
Monitoring should focus on behaviour, not merely connectivity. A trusted integration account may still behave abnormally. Unexpected transaction volumes, unusual request patterns, new operations or attempts to access unrelated services should be visible.
And perhaps most importantly, the organisation should be able to isolate the partner quickly.
If that partner is compromised, can credentials be revoked? Can the integration be suspended? Can the affected route be blocked without disrupting unrelated critical services?
That is where resilience becomes part of the integration design.
Trust Should Be Limited By Blast Radius
This is where the discussion connects naturally to another principle: The Strongest Architecture Is The One That Limits Blast Radius.
A trusted partner should not automatically inherit access to a wide part of the environment.
If one compromised integration credential can reach several internal systems, the blast radius is large. If that same integration is restricted to one service, one API and a narrow set of functions, the impact is much easier to contain.
The security architecture should therefore ask not only whether the partner is trusted, but how much authority that trust creates.
Trust should be specific.
Trust should be limited.
Trust should be revocable.
And trust should never provide more access than the business process actually requires.
The Architecture Review Questions Need To Change
Architecture reviews often ask familiar questions.
Is the communication encrypted? Is the firewall configured? Does the API require authentication? Has the vendor passed its security assessment?
Those questions are necessary, but they are not enough.
A stronger architecture review should also ask:
If this partner is fully compromised tomorrow, what prevents the attacker from using the existing connection to compromise us?
And equally important:
Can we isolate that partner immediately and continue critical business operations safely?
Those two questions reveal far more about the resilience of the design than a simple confirmation that the connection uses encryption and valid credentials.
They shift the discussion from connectivity to survivability.
Final Thoughts
Business integration is unavoidable.
Modern organisations depend on connected ecosystems to operate efficiently.
But connectivity must never be confused with trustworthiness.
A secure architecture should not assume that a trusted partner will always remain secure. It should assume that compromise is possible and make sure the consequences can be contained.
That means limiting privileges, isolating integration paths, monitoring behaviour, reducing blast radius and designing a clear path to revoke trust quickly.
Because an attacker does not always need to find a way through your front door.
Sometimes the easier route is through a door you already opened for someone else.
The objective of enterprise security architecture is not only to protect the organisation from untrusted outsiders. It is also to prevent trusted relationships from becoming uncontrolled attack paths.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.