Security Controls Cannot Fully Repair Poor Architecture
Firewalls, MFA, monitoring and guardrails matter, but they operate inside the architecture. When the design creates excessive trust or authority, controls can only compensate for part of the weakness.
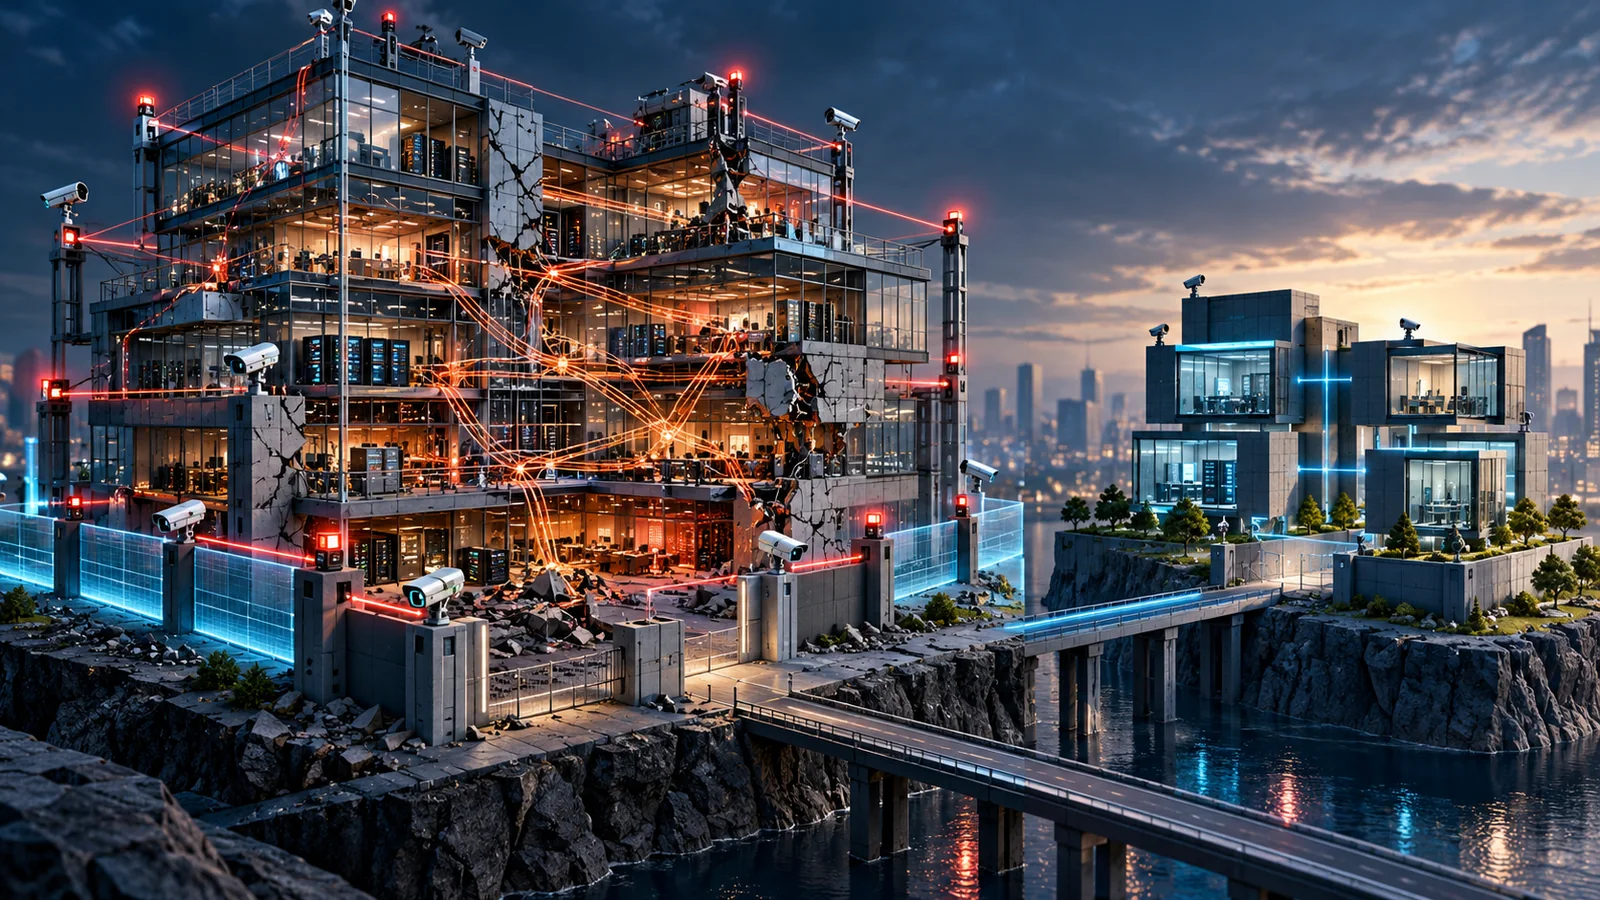
Security programmes often respond to risk by adding another control.
Another firewall rule. Another monitoring tool. Another authentication step. Another alert. Another compensating control.
These measures are useful, and often necessary.
But there is a point where adding more controls stops addressing the real problem.
If the architecture itself creates excessive trust, broad privilege, weak separation or fragile dependencies, security controls can reduce the risk.
They cannot fully repair the design underneath it.
Architecture Defines The Shape Of The Risk
A security control usually protects something that already exists.
A firewall protects a connection. MFA protects an identity. DLP protects data movement. EDR protects an endpoint. SIEM monitors activity.
Architecture decides why those connections exist, which identities have access, where data can move and how much authority each component receives.
That distinction matters.
If one application has unrestricted access to several critical databases, monitoring does not change the fact that the application has broad authority.
If production and non-production share privileged identities, MFA may protect those accounts but it does not remove the shared trust relationship.
If a third-party integration connects directly to critical internal services, encryption protects the communication but does not change what happens if the partner itself becomes compromised.
Security controls operate inside the architecture.
They do not replace it.
Excessive Trust Is An Architectural Problem
Trust is one of the clearest examples.
In Every Trust Relationship Is An Attack Path, I argued that every connection should be understood not only as connectivity, but also as a trust decision.
If that trust is too broad, controls placed around it may not remove the underlying weakness.
Imagine a service account with access to ten applications when the business process only requires access to two.
The credential can be placed in a vault. Its use can be monitored. It can be rotated frequently. Alerts can be generated when behaviour changes.
Those are all useful controls.
But the architecture still contains unnecessary trust.
The stronger solution is to reduce the authority itself.
Security Tools Cannot Shrink Blast Radius By Themselves
The same problem appears with privilege concentration.
Suppose one administrator account can control cloud infrastructure, identity services, backups and security tooling.
MFA helps. Privileged access management helps. Session monitoring helps.
But the underlying architectural problem remains: too much authority is concentrated behind one identity.
As discussed in The Strongest Architecture Is The One That Limits Blast Radius, good architecture aims to ensure that one compromise does not automatically become an enterprise-wide compromise.
That requires separation of administrative domains, limited privilege, independent recovery access and smaller trust boundaries.
Controls then reinforce the architecture rather than compensate for it.
Cloud Can Scale Poor Architecture Too
Cloud environments make this even more important.
A broad role can suddenly reach hundreds of resources. A shared network can connect workloads that were never intended to trust one another. A single secret can be reused across multiple services. A central control plane can create significant concentration risk.
It is possible to deploy excellent cloud security tooling around all of this.
But if the underlying boundaries remain weak, the organisation may still be one compromised identity away from a much larger incident.
Moving to cloud should therefore not mean recreating the old data-centre architecture inside another provider's infrastructure.
Cloud is an opportunity to redesign trust, segmentation, identity and recovery from the beginning.
If that opportunity is missed, security teams may spend years adding controls around structural weaknesses created much earlier.
AI Creates The Same Problem
AI introduces a new version of this challenge.
An AI agent may be protected by prompt filtering, content inspection, model guardrails and monitoring.
But if that same agent has broad access to databases, APIs, MCP servers and business applications, the architecture still carries a large blast radius.
The first question should not be:
Which AI security product should we deploy?
It should be:
What should this AI actually be allowed to reach?
In Every AI Use Case Should Have an Owner, a Boundary and a Kill Switch, the boundary matters precisely because capability needs to be constrained before behaviour is monitored.
If the architecture gives an AI agent too much authority, no prompt guardrail can guarantee that authority will never be misused.
Capability should be limited before controls are layered around it.
Monitoring Is Not The Same As Containment
Another common mistake is assuming that visibility compensates for weak design.
It does not.
Knowing that an attacker is moving does not necessarily stop them from moving.
Knowing that a privileged identity has been compromised does not reduce what that identity can access.
Knowing that a partner integration is behaving strangely does not help enough if the connection cannot be isolated without disrupting critical business operations.
Monitoring is necessary.
But the architecture must also provide mechanisms to contain the event.
This is closely related to the problem discussed in Your Trusted Business Partner Is Compromised. Are You Next?.
If a trusted connection becomes hostile, the organisation should already know how to isolate it.
That ability has to be designed in advance.
An alert cannot create a missing containment boundary after the attack has started.
Attack Surface Is Usually Created Earlier
This is why security needs to engage during architecture and design, not only before go-live.
In Attack Surface Is Designed Long Before Go-Live, the central argument is that attack surface is often created through early decisions about trust, connectivity, privilege and dependency.
Once those decisions are embedded into applications and business processes, changing them becomes more difficult and expensive.
The later security enters the process, the more likely the response becomes another compensating control.
Sometimes that is unavoidable.
Legacy systems exist. Business deadlines exist. Technology constraints are real.
But organisations should recognise the difference between a security control and a compensating control for architectural weakness.
They are not the same thing.
Good Architecture Makes Controls More Effective
None of this means security controls are less important.
Strong architecture actually makes them more effective.
MFA is more valuable when privileged identities are already separated.
Network controls are more effective when security domains are clearly defined.
DLP works better when sensitive data flows are understood.
AI guardrails are more effective when agents already have limited authority.
Monitoring is more useful when the architecture provides clear trust boundaries and meaningful containment points.
Architecture defines the structure.
Controls enforce, monitor and strengthen that structure.
The problem begins when controls are expected to compensate indefinitely for poor decisions underneath them.
Final Thoughts
Security controls are essential.
But they should not become a substitute for architecture.
A firewall cannot fully repair excessive trust.
MFA cannot fully repair excessive privilege.
Monitoring cannot fully repair excessive blast radius.
DLP cannot fully repair uncontrolled data movement.
An AI guardrail cannot fully repair an agent with unnecessary authority.
And another security product cannot always repair a system that was never designed to survive compromise.
Good security architecture reduces the problem before controls are applied.
It limits trust.
It limits authority.
It creates boundaries.
It contains failure.
Then security controls become what they should be: reinforcement rather than compensation.
Security controls cannot fully repair poor architecture.
Question assumptions. Share knowledge. Build trust.
Share this article
If this perspective was useful, share it with your network.